wp2shell: Critical WordPress Unauthenticated to Remote Code Execution Vulnerability
It’s rare for WordPress itself to have CVEs. CVE-2026-63030 and CVE-2026-60137 combine to create the critical unauthenticated to RCE vulnerability wp2shell.
Jason has a passion for asking “what-if” questions and for trying to “break” software and test how it responds to unintended uses. Jason has a background in System Administration and Security Engineering in the financial sector. He holds both defensive and offensive certifications including OSCP, PNPT, GCIH, CASP+, and is Splunk Certified. When he’s not spending his time taking new training courses, he loves spending time with his wife and kids and occasionally working on an IoT project to automate some aspect of their greenhouse or chicken coop.
It’s rare for WordPress itself to have CVEs. CVE-2026-63030 and CVE-2026-60137 combine to create the critical unauthenticated to RCE vulnerability wp2shell.
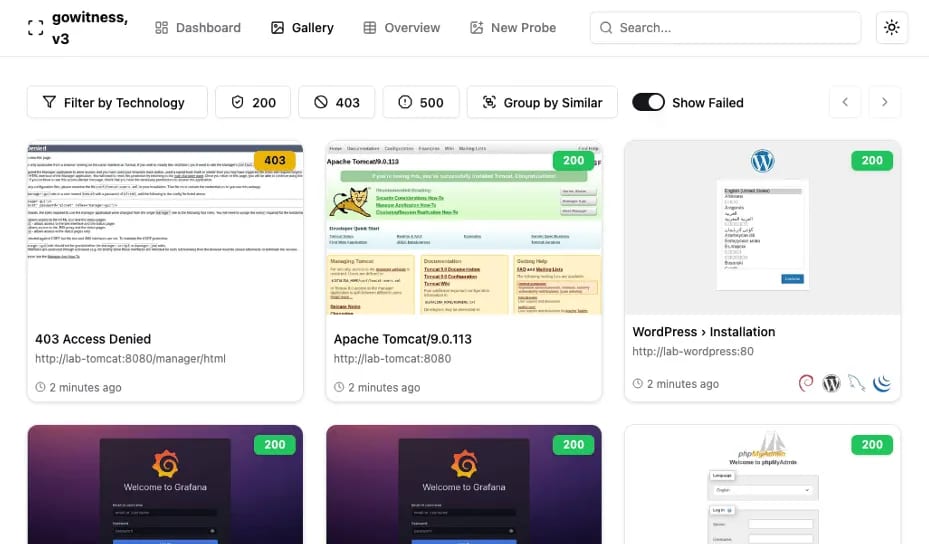
Enumerating webpages during an internal network pentest can be a large task, but GoWitness makes it easy to focus on high value webpages. Learn how it works.
The usbliter8 SecureROM exploit is big news for jailbreaking iPhones. This hardware vulnerability cannot be fixed with a software update.
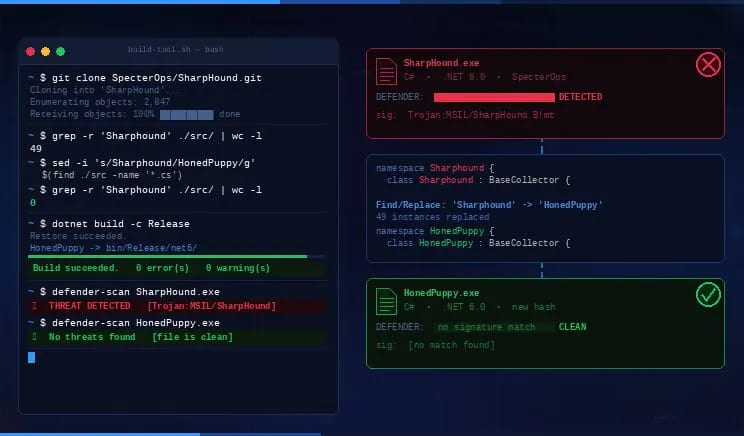
Endpoint security detects many malicious files created with pentest tools, but pentesters can sometimes bypass this by rebuilding source code. Learn how here.
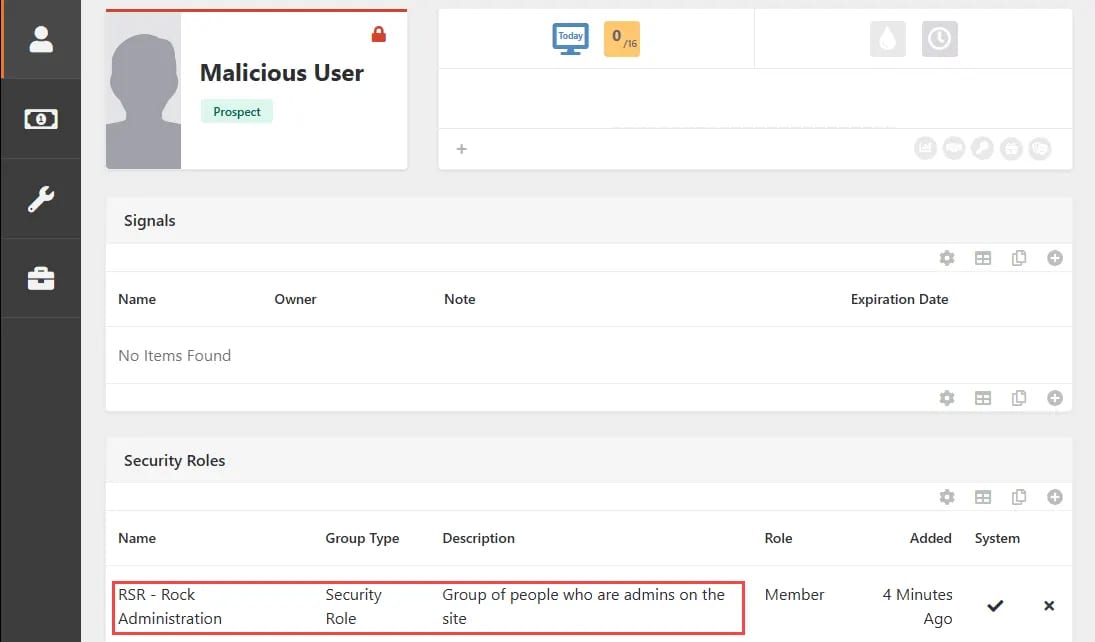
Raxis Lead Pentester Jason Taylor recently discovered CVE-2026-36748, a high-risk XSS vulnerability in Rock RMS that allows privilege escalation to admin.
CVE-2026-31431, dubbed Copy Fail, allows privilege escalation to root on Linux distros missing the latest kernel patches. Learn what to do in this blog.
Last week’s supply chain attack caused many users of the WordPress and Joomla plugin Smart Slider 3 Pro to inadvertently patch to a malicious version.
Jason Taylor brings highlights reptyr in our Cool Tools series, showing how to take a long-running process, like an Nmap scan, and move it to a new screen.
When a Raxis pentester Jason Taylor found a suspicious sponsored search result, he broke down the code it would have run and discovered it was malware.
With exploit code available for the vulnerabilities in Eaton’s xComfort Ethernet Communication Interface, Jason Taylor recommends replacing or isolating.
Raxis’ Jason Taylor is back with a detailed tutorial on performing both manual and automated DNS exfiltration attacks for pentesting.
Raxis Lead Penetration Tester Jason Taylor’s in-depth tutorial explains setting up a server for DNS exfiltration. Check back next month to run the attack.
21 posts by Jason Taylor.