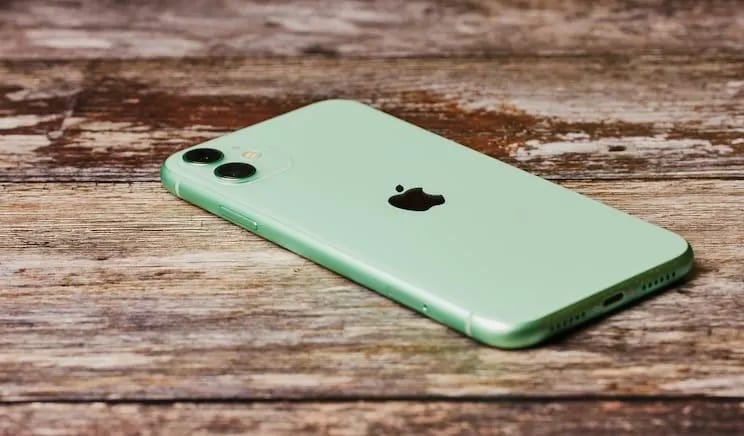
Security researchers at Paradigm Shift recently announced the usbliter8 SecureROM exploit that affects Apple A12 and A13 chipsets. The proof-of-concept allows for bypassing Apple’s protections within the SecureROM boot process and allows for code execution on a myriad of older iPhones and iPads. Of particular note is that the iPhone 11, which will support iOS 27, is the newest iPhone affected by this vulnerability.
From an offensive security perspective, this could lead to a jailbreak for newer, but still old, iPhones such as the iPhone 11. This could allow for full access during mobile app penetration tests, although currently there is no full jailbreak available that uses this vulnerability.
What This Means for iPhone 11 Users
From a consumer perspective, this means the iPhone 11, a device that will be receiving the latest iOS 27 later this year, will be affected by a hardware-level exploit that cannot be patched via software.
Taking advantage of the exploit does require plugging the affected device into a Raspberry Pi via a Lighting cable. This decreases the risk of this exploit being used against a normal day-to-day user of an iPhone 11. However, this could open these devices up to further inspection in situations where a phone is removed from the owner, such as during international travel when law enforcement agencies may confiscate devices during interviews.
If you use an iPhone 11 or older and travel frequently, consider upgrading to a newer device to protect yourself from this risk.