Rooting a Google Pixel 8 for Mobile App Penetration Testing
Principal Penetration Tester Andrew Trexler takes us step-by-step through the process of rooting a Google Pixel for mobile application pentesting.
Andrew graduated from the University of Pittsburgh with a degree in Information Science where he focused on networking and security. He continued his education by obtaining the Offensive Security Certified Professional (OSCP) and the eLearnSecurity Junior Penetration Tester (eJPT) certifications. When not participating in capture the flag events, Andrew works as a pyrotechnic operator setting up and shooting firework shows in the Pittsburgh area.
Principal Penetration Tester Andrew Trexler takes us step-by-step through the process of rooting a Google Pixel for mobile application pentesting.
BloodHound’s Community Edition has everything a penetration tester needs to enumerate relationships in a domain in order to gain more access, even Domain Admin.
CVE-2026-0300 is a critical buffer overflow vulnerability in Palo Alto’s PAN-OS software. Discover if you are affected and what to do now.
So you got DA on your red team or internal network penetration test. Here are the five things that Principal Penetration Tester Andrew Trexler does next.
On a recent web app pentest, Andrew Trexler used AI to find client-side code that stopped his brute-force attack then used AI again to thwart that code.
Andrew Trexler looks at a recently discovered public database of stolen usernames and passwords and what you can do now to protect your access and information.
Though hacker groups claimed to have access to internal systems, CrowdStrike announced they fired an insider who shared external screens with the attackers.
Raxis Principal Penetration Tester Andrew Trexler walks through the many uses of Kerbrute from user enumeration to brute-forcing and password spraying.
A recent successful phish allowed attackers to run malware targeting cryptocurrency transactions on various blockchains, but fast reporting limited the damage.
Principal Penetration Tester Andrew Trexler got curious how easy it might be to customize a phish to a specific website using AI. The answer? Very easy.
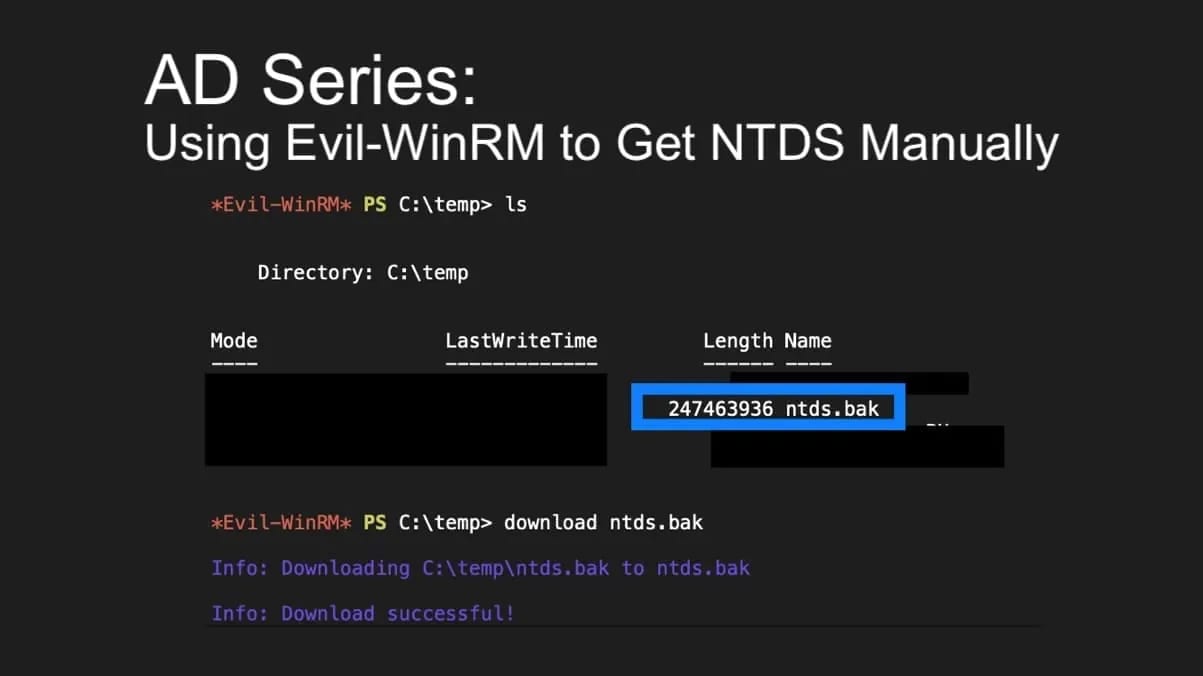
Principal Penetration Tester Andrew Trexler’s Active Directory series is back, showing how to use Evil-WinRM to copy NTDS.dit manually in penetration tests.
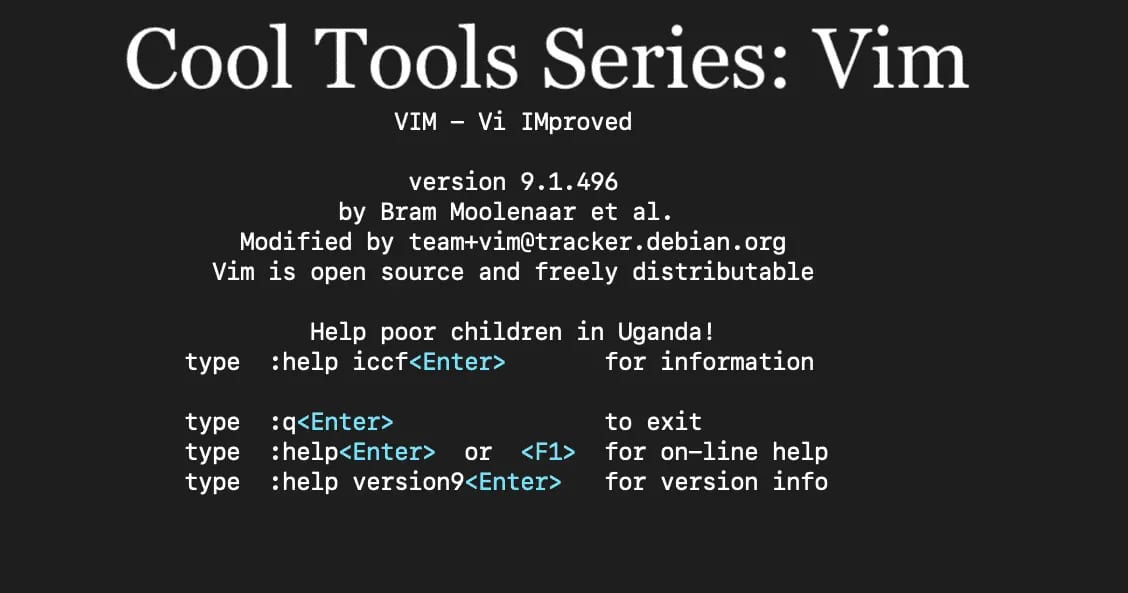
Principal Penetration Tester, Andrew Trexler, dives into Vim, a powerful command line tool for text files, and shows useful commands for penetration testing.
24 posts by Andrew Trexler.