Brian brings to Raxis a rich and varied background in Information Technology spanning more than 20 years. Sought after by clients for his unique blend of business acumen and technical prowess, Brian has consistently delivered value to hundreds of organizations spanning the globe throughout his career. Brian is Raxis’ CTO and currently leads the Raxis Penetration Testing and Social Engineering team.
The Raxis pentesting team is at DefCon in Vegas this weekend. It’s an awesome conference that has lessons and contests for everything from lock picking and car hacking to new network and application exploits that our team may try on your next penetration test. For those of you who may not have atten
Wednesday thousands of car dealerships across North America experienced a cyberattack resulting in widespread outages and significant operational degradation.
Password length requirements are a key part of password security, but, with PCI, NIST, OWASP, and CIS offering different recommendations, what length is best?
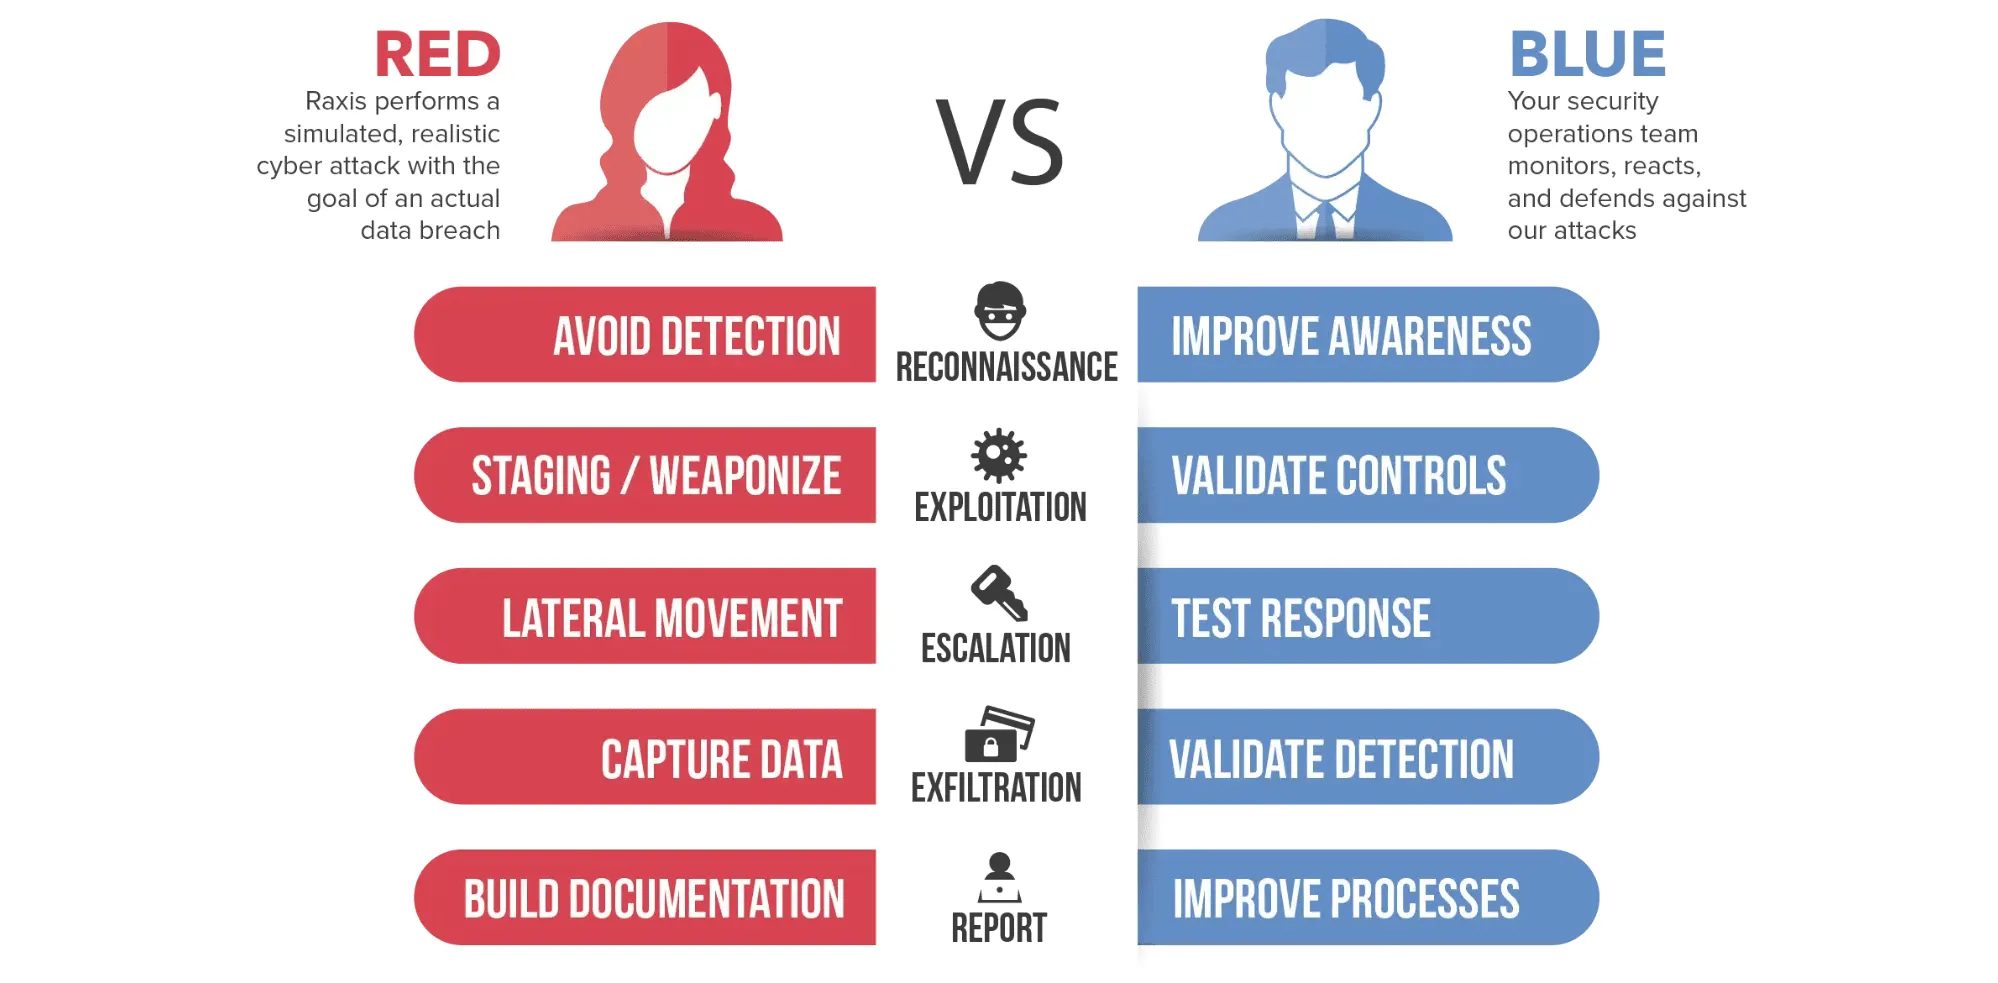
Red Teams, Blue Teams, and Purple Teams are cybersecurity terms describing different approaches to testing & improving security measures within an organization.
A new nationwide cyberattack appears to be targeted at U.S. based hospitals, clinics, and other health care facilities. Healthcare on heightened alert.
Network segmentation can be an important line of defense against hackers. Raxis’ CTO Brian Tant explains why in this continuation of our Top 10 Vulnerabilities series.
Raxis uses cookies to measure how the site is used and to connect your visit with our team
when you reach out. Necessary cookies always run. Change your choice any time from Cookie
settings in the footer. See our Privacy Policy.